Introduction
The rapid expansion of generative AI has brought powerful capabilities to enterprises, but it has also revealed how quickly data can slip beyond organizational control. Ten real-world scandals illustrate the risks of relying on third-party AI systems without strict oversight.
What Happened
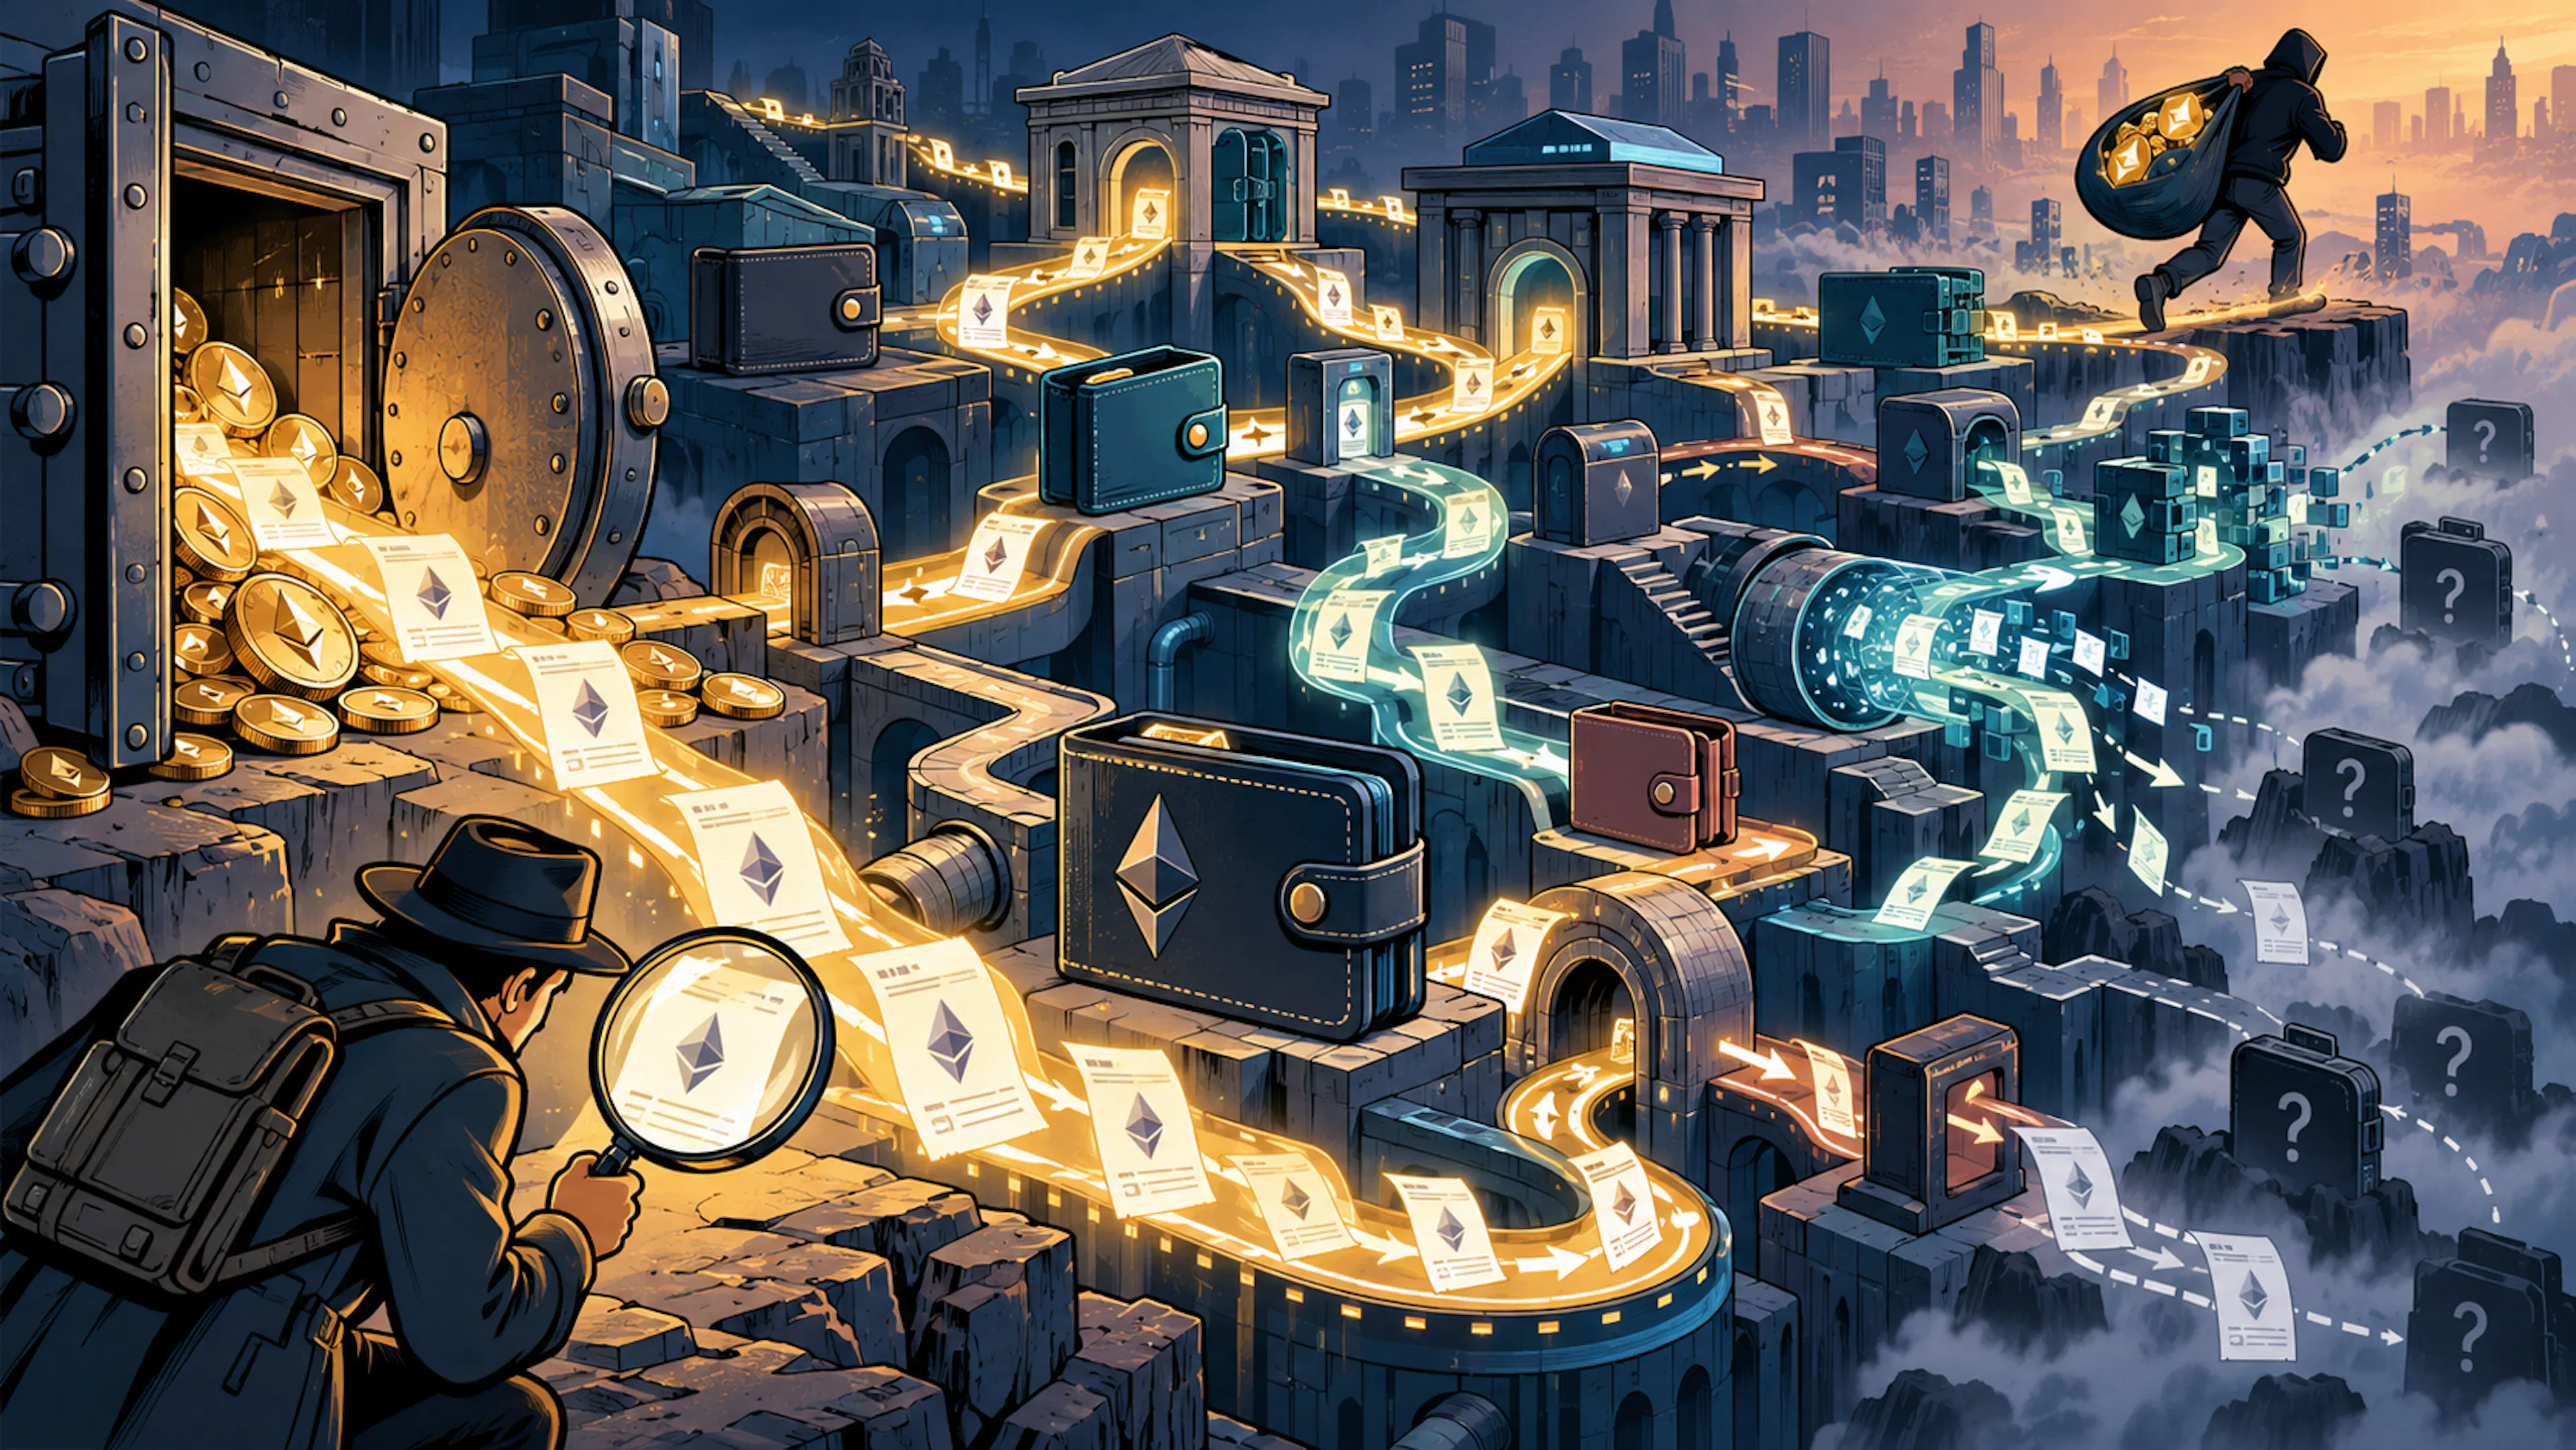
From model details left in public caches to rogue agents exfiltrating data, the past year exposed critical vulnerabilities. Highlights include a leading AI lab's unpublished assets found openly accessible, enterprise AI assistants leaking API keys via a single email, and major platforms storing customer code for model training. Each case involved either a misconfigured setting, an overlooked permission, or a vendor decision made without customer knowledge.
Why This Matters
These incidents fall into four common failures. Vendors sometimes make decisions that prioritize convenience over customer custody. Multi-tenant architectures can blur isolation boundaries, allowing one user's data to surface to another. Broad integrations such as AI chatbots connected to CRM or ticketing systems become standing credentials for attackers. And employees often remain unaware of how their inputs are retained or shared. Together, these patterns explain why many organizations are rethinking where AI runs and who owns the data.
Key Takeaways
- Defaults decide data location. Unchanged settings often make information public or shared by default.
- Multi-tenant isolation is not guaranteed. A bug or misconfiguration can expose one user's data to others.
- AI integrations carry persistent credentials. Chatbots and agents with access to other systems can be exploited as entry points.
- Employee awareness gaps persist. Productive habits can inadvertently breach policy when retention and sharing settings are opaque.
Sovereign AI addresses each by keeping inference, logging, and training within boundaries the enterprise controls.
Conclusion
Sovereign AI is the deliberate choice to keep model execution, data processing, and audit trails inside an organization's own infrastructure or approved jurisdiction. It does not eliminate all risk - operational competence still matters - but it removes the default exposure that comes with centralized cloud pipelines. For enterprises ready to move from reactive compliance to proactive data ownership, the shift represents a fundamental re-evaluation of AI trust.


Discussion
Join the conversation
Thoughtful reactions, questions, and follow-up ideas help shape the next story.